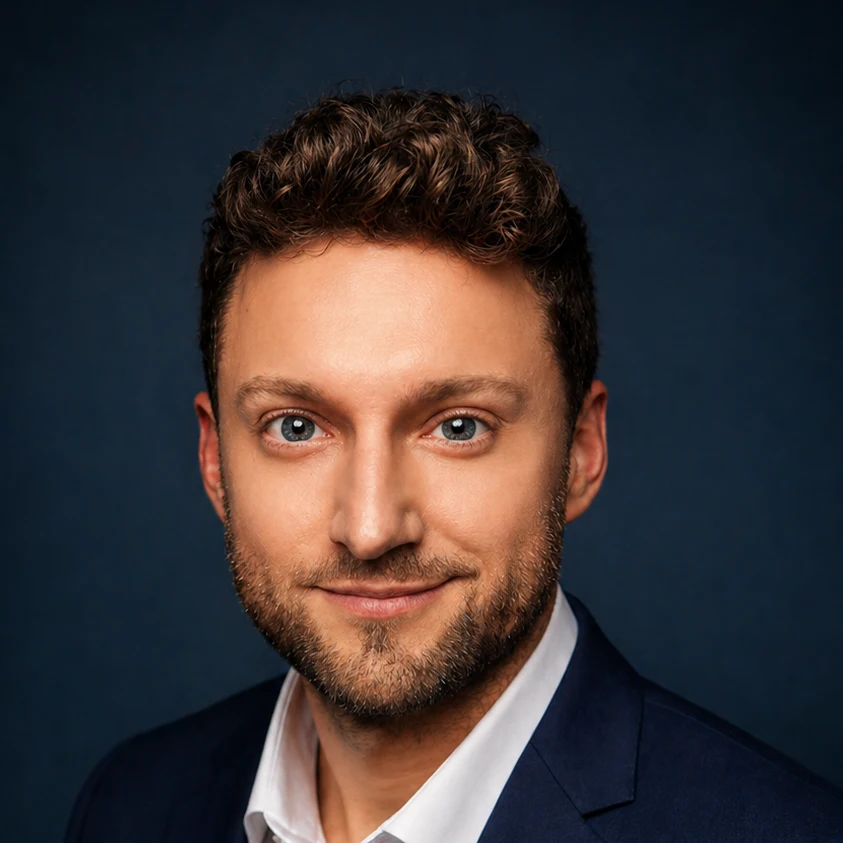
Matthieu Guilpin.

Chief Information Security Officer

Protect what matters.
Build trust.
Enable growth.

CurrentlyCISO at Pelico
Portrait of Matthieu Guilpin
SECURITY LEADERSHIPSAAS & AI
01 / EXPERTISE & APPROACH

Security built around
business priorities.

My approach starts with understanding the business and its risks, then translating those priorities into focused security programs that strengthen trust, resilience and performance.

01

Understand what drives security priorities

KEY INPUTS
01 / BUSINESS

Business & Technology Strategy

Business objectives, product roadmap, operational needs, technology transformation and market opportunities.

02 / CUSTOMERS

Customer & Contractual Requirements

Security due diligence, customer expectations, contractual commitments and market access.

03 / OBLIGATIONS

Regulatory & Assurance Requirements

Applicable regulations, certification standards and independent assurance obligations.

04 / EXPOSURE

Risk & Threat Landscape

Internal and external risk assessments, evolving threats and business exposure.

INFORM THE SECURITY STRATEGY ↓
02

Turn strategy into execution

CORE PILLARS
PILLAR 01

Governance,
Risk & Trust

Building the governance and assurance foundations that make security accountable, demonstrable and trusted.

Security governanceRisk & third partiesISO 27001 / SOC 2Customer assuranceAwareness & cultureBusiness continuity
PILLAR 02

Security Engineering
& Operations

Protecting technology, products and people through practical security engineering and operational capabilities.

Security teamsSOC & incident responseVulnerability managementCloud & CNAPPAppSec & DevSecOpsIdentity & access

↗ Security Leadership

Executive reporting, security transformation and leadership of teams of up to six people.

↗ AI Security & Governance

AI risk and governance experience, including leading an ISO 42001 certification program at Jus Mundi.

DELIVER BUSINESS VALUE ↓
03

Deliver outcomes that matter

BUSINESS OUTCOMES

Customer Trust & Market Access

Help win, retain and reassure customers.

Demonstrable Compliance

Demonstrate conformity with certifications, regulations and contractual obligations.

Risk Reduction

Reduce the likelihood and impact of incidents.

Operational Resilience

Maintain critical operations and respond to, recover from and learn from incidents.

Secure Business Enablement

Enable innovation, dependable operations and sustainable transformation.

CREDENTIALSCISMCCISOCCSKISO 27001 Lead Implementer
02 / EXPERIENCE

From strategy
to execution.

Security leadership across enterprise SaaS, legal technology and AI-powered industrial operations.

Pelico

September 2026 – Present
Chief Information Security Officer

Leading cybersecurity and trust for an AI-powered operations platform serving industrial organizations.

INDUSTRIAL TECHB2B SAASAI

Jus Mundi

March 2025 – August 2026
Chief Information Security Officer

Led security assurance and AI governance in legal technology, including the ISO 42001 certification program.

LEGAL TECHAI GOVERNANCESAAS

Mirakl

2019 – 2025
Chief Information Security Officer

Built and scaled the security function, supporting enterprise assurance and international SaaS operations.

ENTERPRISE SAASSECURITY LEADERSHIP
03 / PUBLICATIONS

Perspectives
from the field.

Selected writing and interviews on security leadership, trust and AI governance.

INTERVIEW · DAILY JUS

Building security into legal AI

A conversation about security leadership, customer trust and responsible AI.

Read the interview ↗
PUBLICATIONS · MIRAKL

Scaling enterprise security

Articles about security assurance and enterprise trust in SaaS.

Explore the articles ↗
LET'S CONNECT

Security is a business conversation.

Always interested in exchanging perspectives on cybersecurity, SaaS and AI governance.